Upgrade your PHP immediately! CVE-2026-109618 and CVE-2026-109619
URGENT: Critical PHP Vulnerabilities (CVE-2026-109618 and CVE-2026-109619) - Action Required
What's Going On
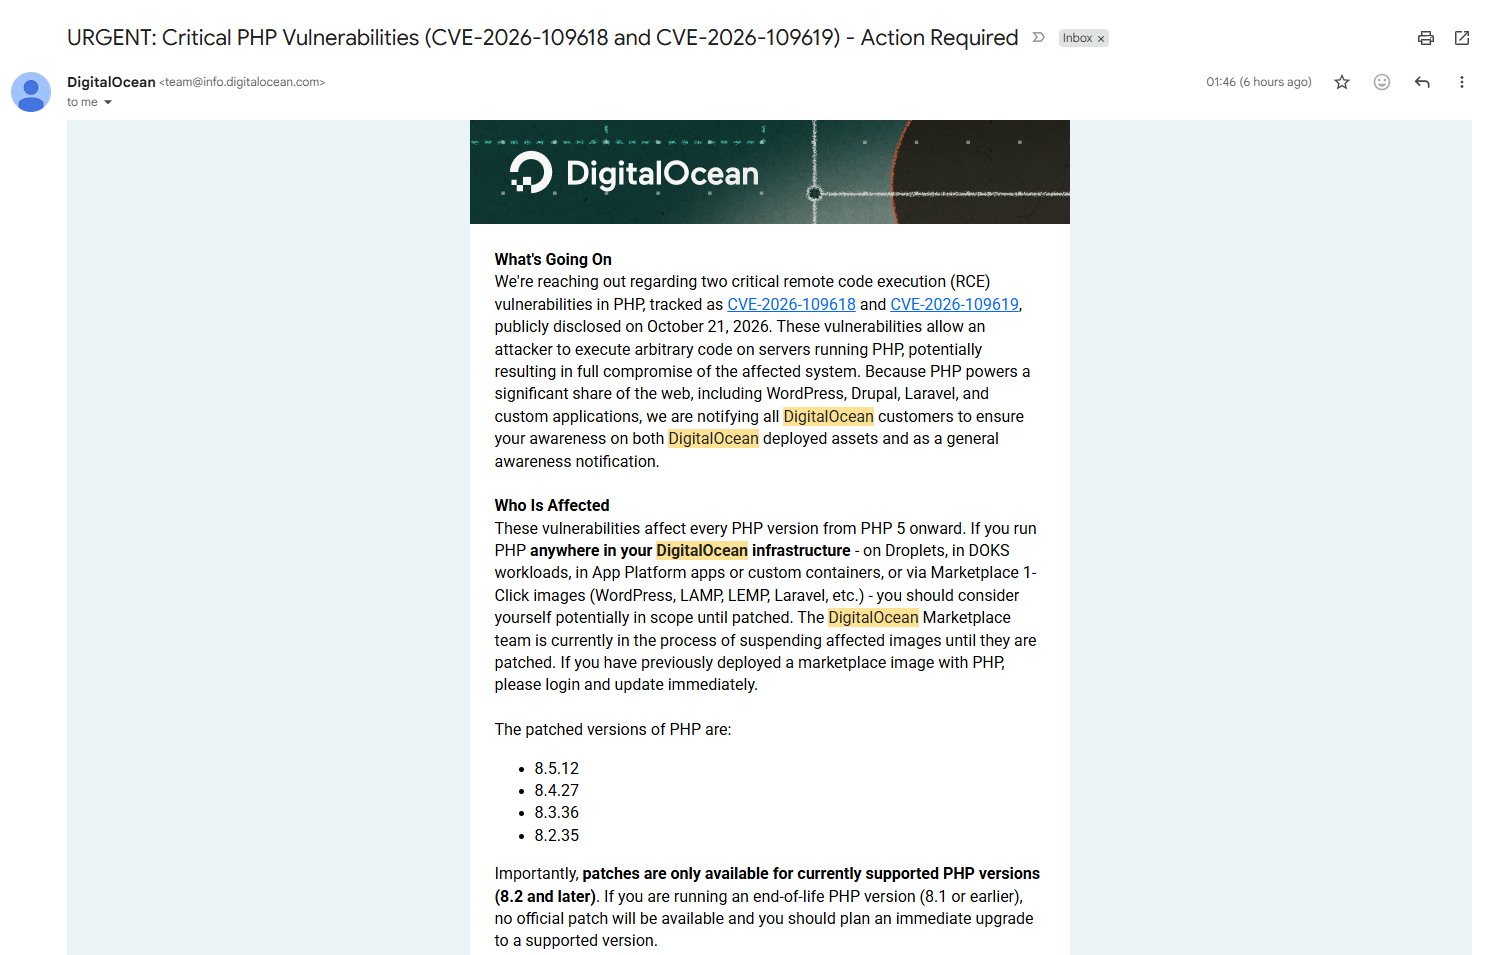
We're reaching out regarding two critical remote code execution (RCE) vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619, publicly disclosed on October 21, 2026. These vulnerabilities allow an attacker to execute arbitrary code on servers running PHP, potentially resulting in full compromise of the affected system. Because PHP powers a significant share of the web, including WordPress, Drupal, Laravel, and custom applications, we are notifying all DigitalOcean customers to ensure your awareness on both DigitalOcean deployed assets and as a general awareness notification.
Who Is Affected
These vulnerabilities affect every PHP version from PHP 5 onward. If you run PHP anywhere in your DigitalOcean infrastructure - on Droplets, in DOKS workloads, in App Platform apps or custom containers, or via Marketplace 1-Click images (WordPress, LAMP, LEMP, Laravel, etc.) - you should consider yourself potentially in scope until patched. The DigitalOcean Marketplace team is currently in the process of suspending affected images until they are patched. If you have previously deployed a marketplace image with PHP, please login and update immediately.
The patched versions of PHP are:
8.5.12
8.4.27
8.3.36
8.2.35
Importantly, patches are only available for currently supported PHP versions (8.2 and later). If you are running an end-of-life PHP version (8.1 or earlier), no official patch will be available and you should plan an immediate upgrade to a supported version.
What You Should Do Now
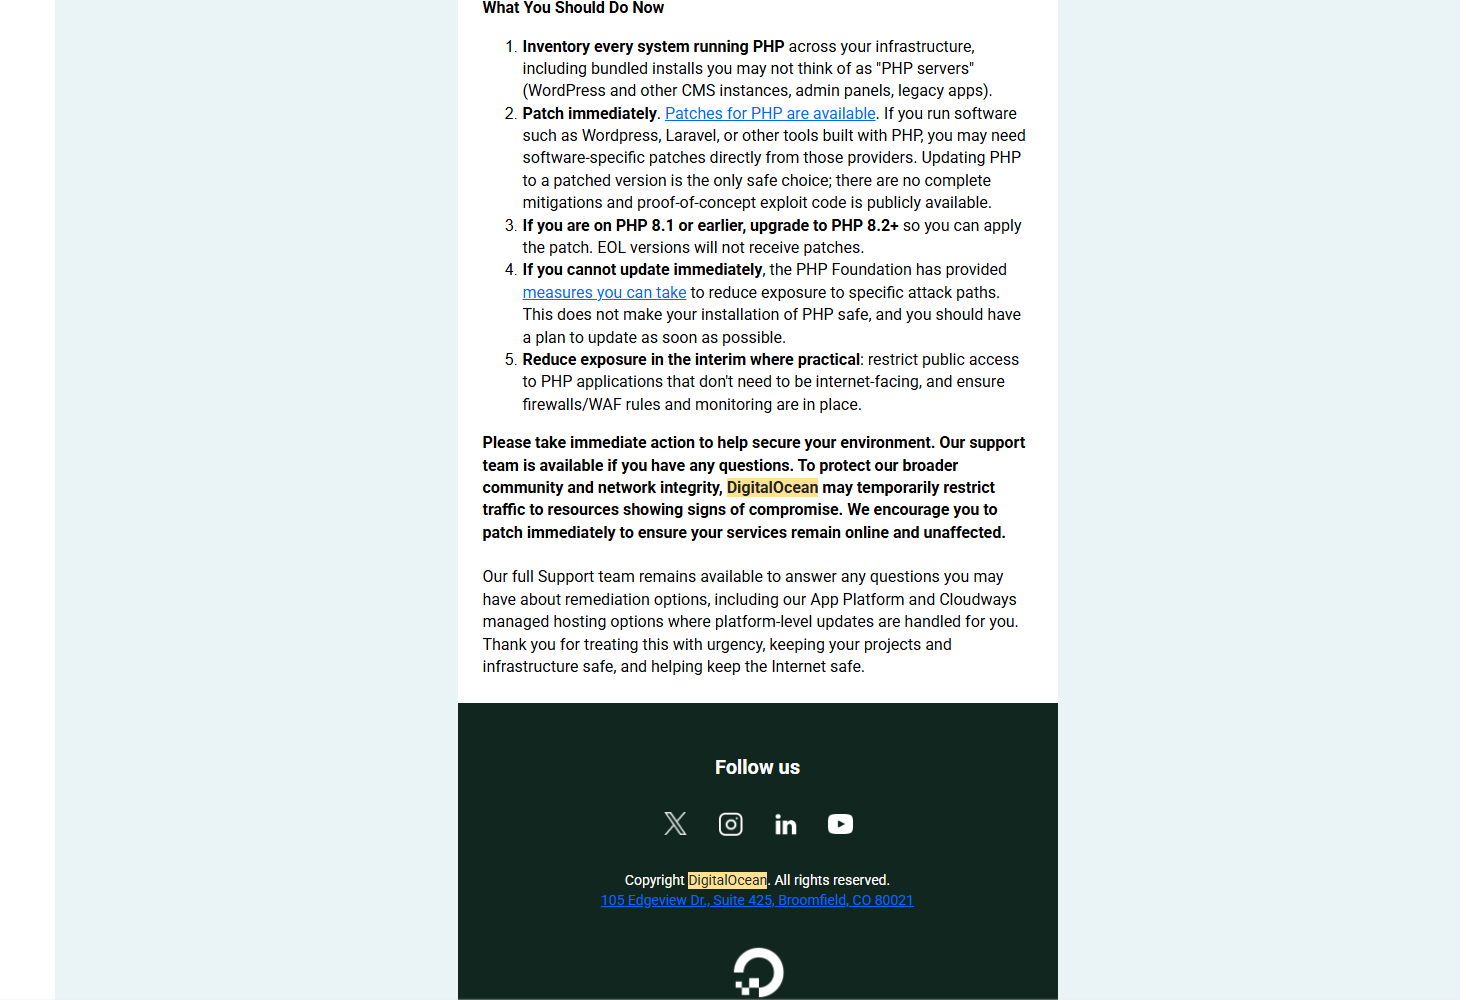
Inventory every system running PHP across your infrastructure, including bundled installs you may not think of as "PHP servers" (WordPress and other CMS instances, admin panels, legacy apps).
Patch immediately. Patches for PHP are available. If you run software such as Wordpress, Laravel, or other tools built with PHP, you may need software-specific patches directly from those providers. Updating PHP to a patched version is the only safe choice; there are no complete mitigations and proof-of-concept exploit code is publicly available.
If you are on PHP 8.1 or earlier, upgrade to PHP 8.2+ so you can apply the patch. EOL versions will not receive patches.
If you cannot update immediately, the PHP Foundation has provided measures you can take to reduce exposure to specific attack paths. This does not make your installation of PHP safe, and you should have a plan to update as soon as possible.
Reduce exposure in the interim where practical: restrict public access to PHP applications that don't need to be internet-facing, and ensure firewalls/WAF rules and monitoring are in place.
Please take immediate action to help secure your environment. Our support team is available if you have any questions. To protect our broader community and network integrity, DigitalOcean may temporarily restrict traffic to resources showing signs of compromise. We encourage you to patch immediately to ensure your services remain online and unaffected.
Our full Support team remains available to answer any questions you may have about remediation options, including our App Platform and Cloudways managed hosting options where platform-level updates are handled for you. Thank you for treating this with urgency, keeping your projects and infrastructure safe, and helping keep the Internet safe.
Action Required: Patch Critical PHP Vulnerabilities
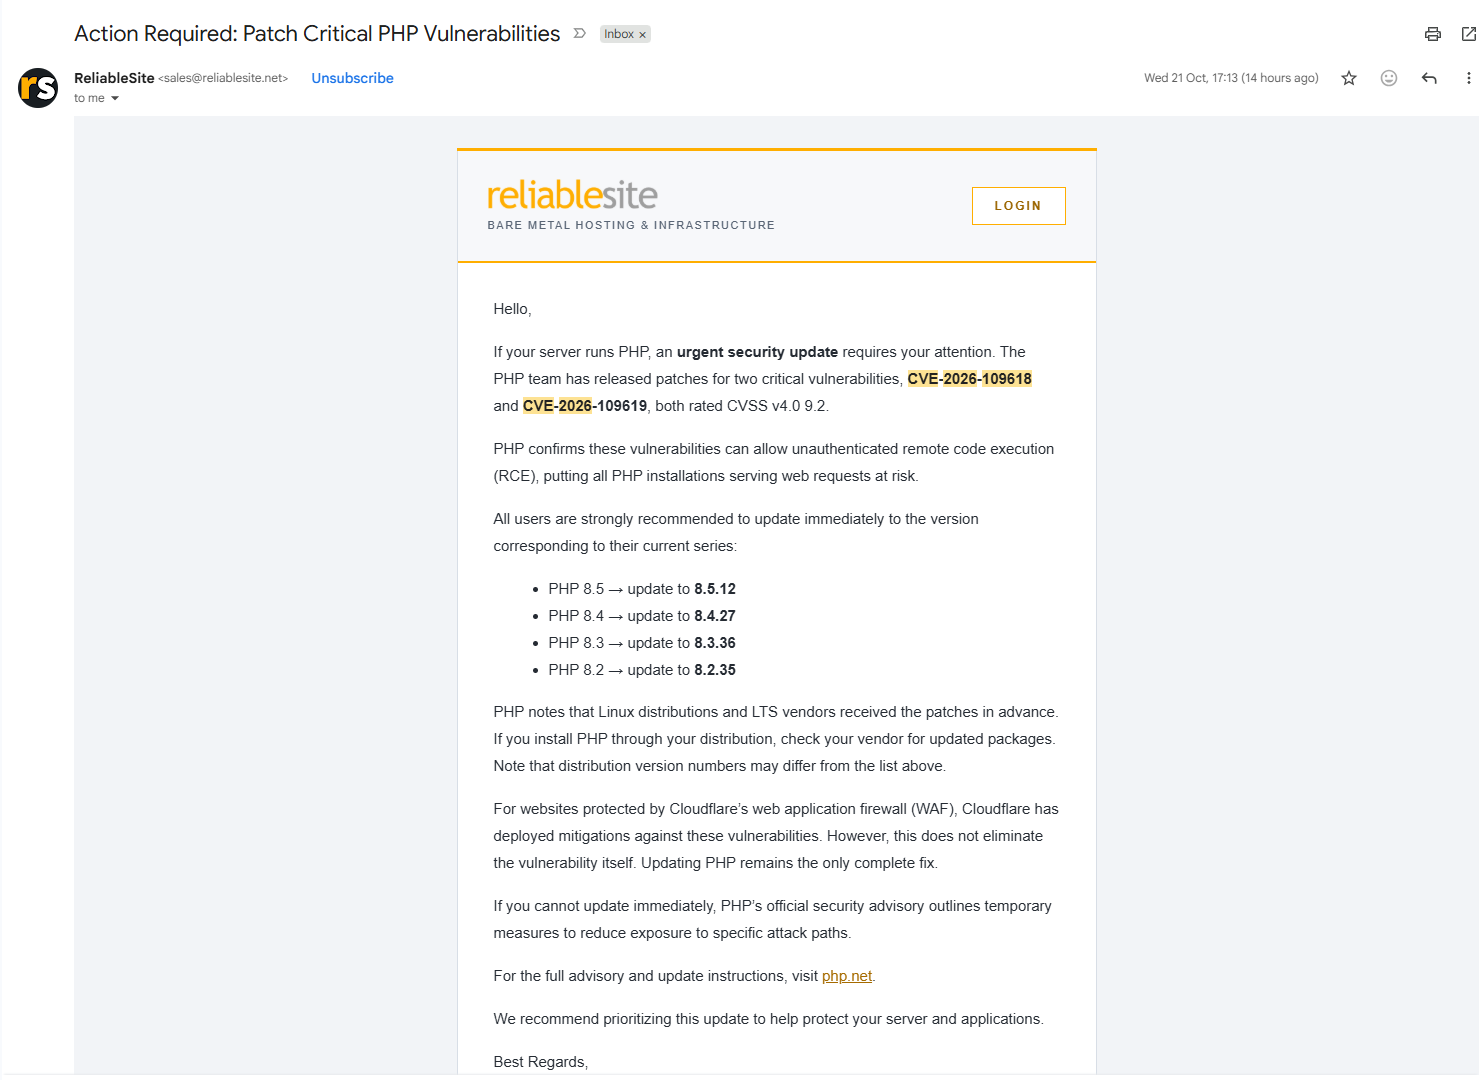
If your server runs PHP, an urgent security update requires your attention. The PHP team has released patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated CVSS v4.0 9.2.
PHP confirms these vulnerabilities can allow unauthenticated remote code execution (RCE), putting all PHP installations serving web requests at risk.
All users are strongly recommended to update immediately to the version corresponding to their current series:
PHP 8.5 → update to 8.5.12
PHP 8.4 → update to 8.4.27
PHP 8.3 → update to 8.3.36
PHP 8.2 → update to 8.2.35
PHP notes that Linux distributions and LTS vendors received the patches in advance. If you install PHP through your distribution, check your vendor for updated packages. Note that distribution version numbers may differ from the list above.
For websites protected by Cloudflare’s web application firewall (WAF), Cloudflare has deployed mitigations against these vulnerabilities. However, this does not eliminate the vulnerability itself. Updating PHP remains the only complete fix.
If you cannot update immediately, PHP’s official security advisory outlines temporary measures to reduce exposure to specific attack paths.
For the full advisory and update instructions, visit php.net.
We recommend prioritizing this update to help protect your server and applications.
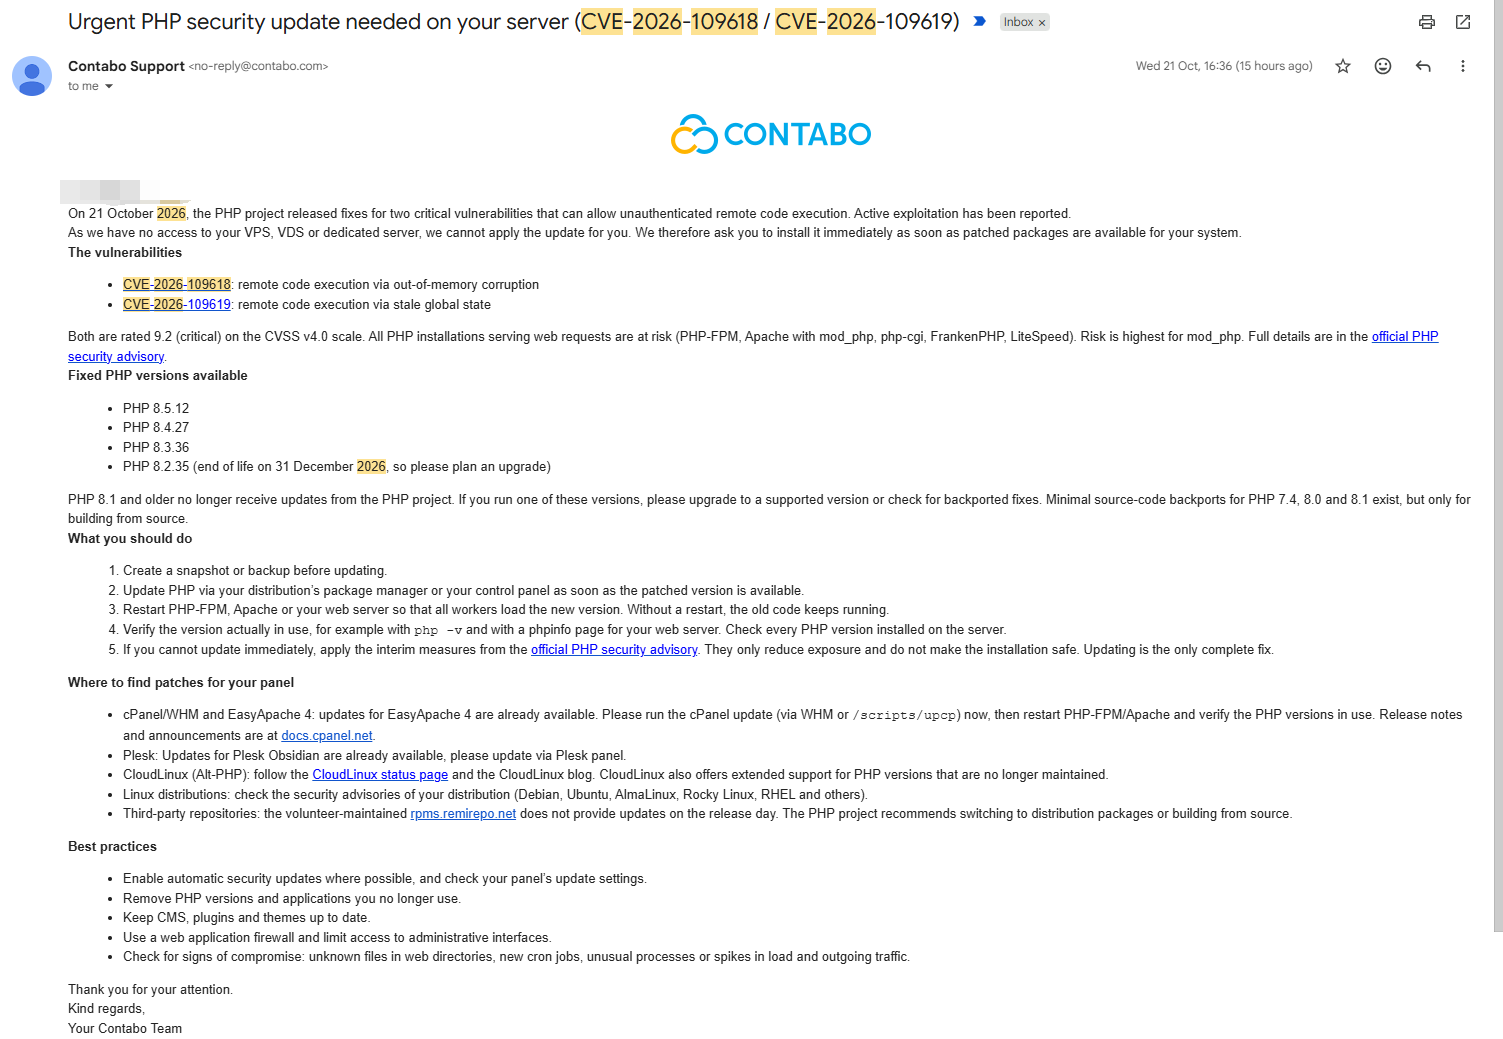
Urgent PHP security update needed on your server (CVE-2026-109618 / CVE-2026-109619)
On 21 October 2026, the PHP project released fixes for two critical vulnerabilities that can allow unauthenticated remote code execution. Active exploitation has been reported.
As we have no access to your VPS, VDS or dedicated server, we cannot apply the update for you. We therefore ask you to install it immediately as soon as patched packages are available for your system.
The vulnerabilities
CVE-2026-109618: remote code execution via out-of-memory corruption
CVE-2026-109619: remote code execution via stale global state
Both are rated 9.2 (critical) on the CVSS v4.0 scale. All PHP installations serving web requests are at risk (PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP, LiteSpeed). Risk is highest for mod_php. Full details are in the official PHP security advisory.
Fixed PHP versions available
PHP 8.5.12
PHP 8.4.27
PHP 8.3.36
PHP 8.2.35 (end of life on 31 December 2026, so please plan an upgrade)
PHP 8.1 and older no longer receive updates from the PHP project. If you run one of these versions, please upgrade to a supported version or check for backported fixes. Minimal source-code backports for PHP 7.4, 8.0 and 8.1 exist, but only for building from source.
What you should do
Create a snapshot or backup before updating.
Update PHP via your distribution’s package manager or your control panel as soon as the patched version is available.
Restart PHP-FPM, Apache or your web server so that all workers load the new version. Without a restart, the old code keeps running.
Verify the version actually in use, for example with php -v and with a phpinfo page for your web server. Check every PHP version installed on the server.
If you cannot update immediately, apply the interim measures from the official PHP security advisory. They only reduce exposure and do not make the installation safe. Updating is the only complete fix.
Where to find patches for your panel
cPanel/WHM and EasyApache 4: updates for EasyApache 4 are already available. Please run the cPanel update (via WHM or /scripts/upcp) now, then restart PHP-FPM/Apache and verify the PHP versions in use. Release notes and announcements are at docs.cpanel.net.
Plesk: Updates for Plesk Obsidian are already available, please update via Plesk panel.
CloudLinux (Alt-PHP): follow the CloudLinux status page and the CloudLinux blog. CloudLinux also offers extended support for PHP versions that are no longer maintained.
Linux distributions: check the security advisories of your distribution (Debian, Ubuntu, AlmaLinux, Rocky Linux, RHEL and others).
Third-party repositories: the volunteer-maintained rpms.remirepo.net does not provide updates on the release day. The PHP project recommends switching to distribution packages or building from source.
Best practices
Enable automatic security updates where possible, and check your panel’s update settings.
Remove PHP versions and applications you no longer use.
Keep CMS, plugins and themes up to date.
Use a web application firewall and limit access to administrative interfaces.
Check for signs of compromise: unknown files in web directories, new cron jobs, unusual processes or spikes in load and outgoing traffic.
Thank you for your attention.
Kind regards,
Your Contabo Team
Steem to the Moon🚀!
- You can rent Steem Power via rentsp!
- You can swap the TRON:TRX/USDT/USDD to STEEM via tron2steem!
- You can swap the STEEM/SBD to SUI via steem2sui!
- You can swap the STEEM/SBD to SOL Solana via steem2sol!
- You can swap the STEEM/SBD to ETH Ethereum via steem2eth!
- You can swap the STEEM/SBD to Tether USDT (TRC-20) via steem2usdt!
- You can swap the STEEM/SBD to TRX (TRON) via steem2trx!
- You can swap the STEEM/SBD to BTS (BitShares) via steem2bts!
- Register a free STEEM account at SteemYY!
- Steem Block Explorer
- ChatGPT/Steem Integration: You can type !ask command to invoke ChatGPT
- Steem Witness Table and API
- Other Steem Tools
Support me, thank you!
Why you should vote me? My contributions
Please vote me as a witness or set me as a proxy via https://steemitwallet.com/~witnesses