Playtime Login Safety: How to Read a URL Before You Sign In
Playtime Login Safety: How to Read a URL Before You Sign In
A technical domain-reading guide for Filipino users: hostname structure, search phrases, lookalike domains, HTTPS limits, and safer account-access habits
Searching for playtime can produce many pages, ads, snippets, and similarly named results. For readers using Playtime Login as an information reference, the safest habit is to separate the words shown in a search result from the actual hostname loaded by the browser. A familiar logo, orange color scheme, or the word “login” does not prove that a page belongs to the destination you intended.
This article focuses on URL anatomy rather than on gambling access. It explains how to read playtimelogin as a search term, how to interpret the unusual phrase www.playtime co.store, and why spaces, subdomains, punctuation, HTTPS, and visually similar characters matter when credentials are involved.
1. Search text and a hostname are different things
A search query can contain spaces, punctuation, escaped characters, and partial brand names. A hostname cannot be interpreted that loosely. Browsers parse a URL into components such as scheme, host, path, query, and fragment. The host is the network location that matters most when you are deciding where a password is about to go.
That distinction is important with a broad word such as playtime. The same word can refer to entertainment, an app, a brand, an article title, or an unrelated business. Search relevance is not identity verification. The FTC warns that scammers can use search results, including paid placements, to imitate trusted companies and steer users to misleading sites.
2. What “playtimelogin” tells you—and what it does not
The compact keyword playtimelogin is useful for search intent because it combines a brand-like term with an account-access action. But removing the space does not create a verified domain. A result containing playtimelogin in the title, path, or page text could still be hosted somewhere entirely different.
When a page asks for credentials, read the hostname from the address bar instead of the headline. Pay attention to the registered domain, not just the first familiar word. A convincing page can place “playtime” inside a subdomain or path while the actual registrable domain belongs to someone else.
3. Why “www.playtime co.store” is not a literal hostname
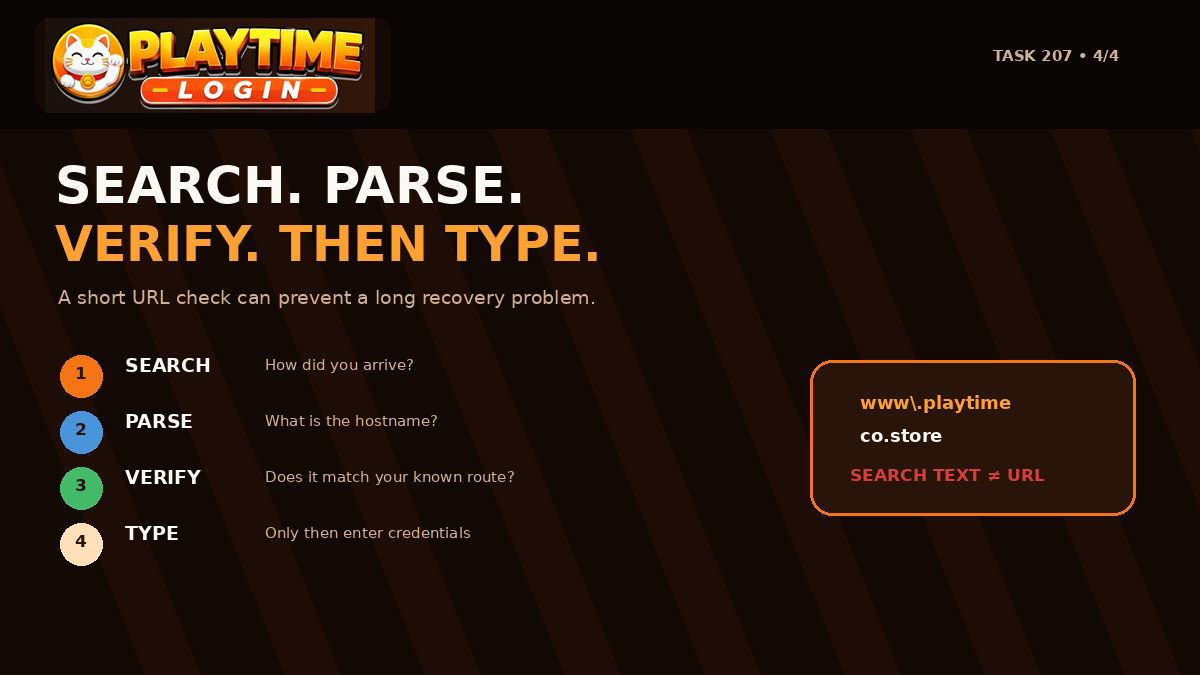
The supporting keyword www.playtime co.store is useful because it demonstrates how SEO-tool output and real URL syntax can diverge. The backslash before the dot is commonly used in regular expressions or escaped text to mean “treat this dot literally.” It is not normally typed into a browser hostname.
The space between “playtime” and “co.store” is another warning that the phrase should be treated as search text, not as a literal web address. The WHATWG URL standard defines hosts and domains using structured labels separated by dots; ordinary spaces are not part of a normal domain label. If the intended string were www.playtime.co.store, that would be a different hostname from playtimelogin.ph and would need to be verified independently.
I did not find reliable public evidence during this task that www.playtime.co.store should be treated as the same destination as Playtime Login. The safe conclusion is not that it is malicious; the safe conclusion is that a different hostname is a different identity until independently verified.
4. Subdomains can make a wrong site look familiar
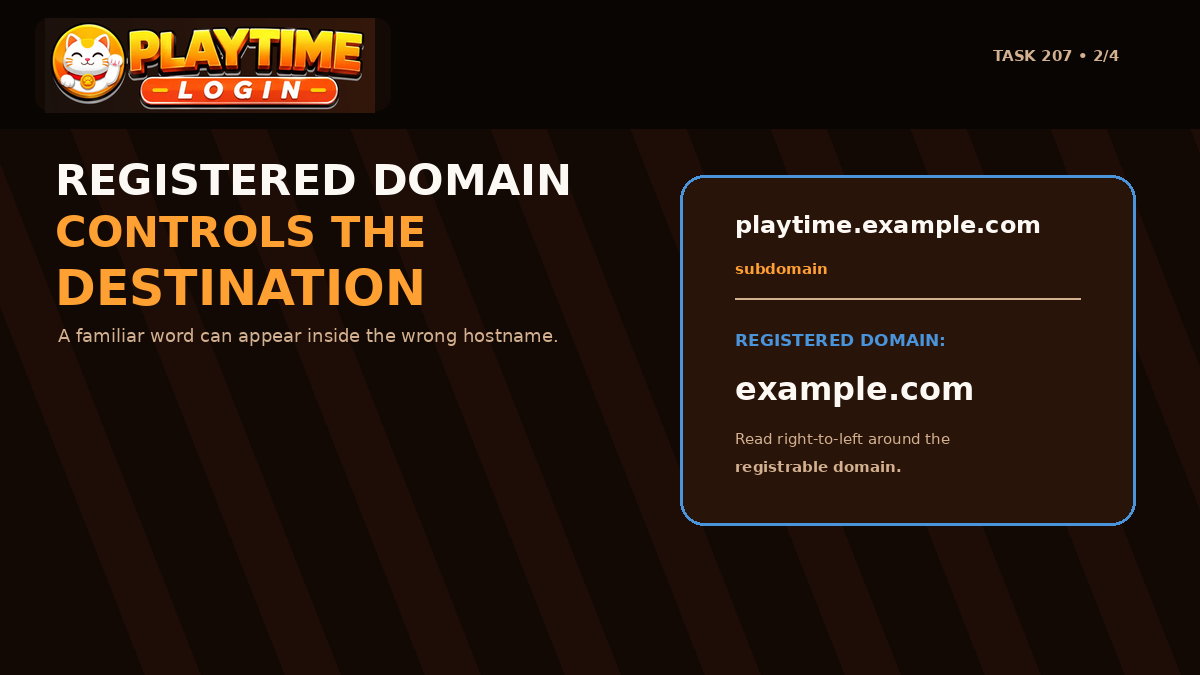
A URL such as playtime.example.com belongs to example.com, not to a separate domain called playtime. Attackers can exploit this by placing a trusted-looking word to the left of the real domain or by appending extra labels after a familiar name. ICANN specifically documents lookalike-domain abuse, including typosquatting and domain-suffix tricks that can make a longer malicious hostname look convincing at a glance.
Mobile screens make this harder because the address bar may be shortened. Before entering a password or OTP, tap the address bar and inspect the full hostname. If the page came from an ad, message, QR code, or shortened link, the need for this check is even stronger.
5. HTTPS is necessary, but it does not prove the brand
A padlock or HTTPS connection means the browser established an encrypted connection to the site named in the certificate. It does not prove that the organization behind that site is the company you expected. A phishing site can also use HTTPS.
Google Safe Browsing adds another layer by warning about known phishing, deceptive sites, malware, and harmful downloads. Google recommends leaving Safe Browsing enabled. If the browser shows a red warning or says a page may be deceptive, do not disable the protection simply because the site looks familiar.
6. Lookalike characters can defeat a quick visual scan
Typos are not the only problem. Visually similar characters can make two different domains appear almost identical. ICANN has long documented homograph attacks in which characters from different scripts or similar-looking letters and numbers are used to imitate another name.
That is why a quick glance at the logo or even the apparent spelling is not enough for a high-risk action. Password managers and passkeys can help because they bind credentials to a site identity rather than to page appearance. Task 191 already covered passkeys, so the useful addition here is the URL-reading layer that comes before any authentication method is used.
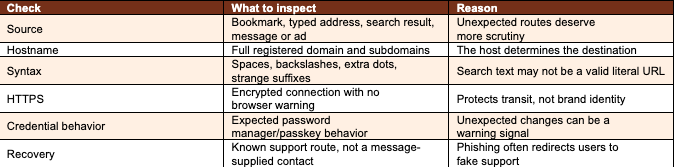
7. A 20-second Playtime URL check
8. Keep account safety separate from promotional claims
The Playtime Login privacy policy can be used as self-published context for how the site describes data handling. It should not be treated as independent proof that every Playtime-branded or similarly named domain has the same controller, security architecture, or privacy practices.
The same separation applies to bonuses, games, payment claims, or VIP language. None of those should influence a domain-verification decision. If a page creates urgency—“claim now,” “verify immediately,” or “account closing”—that is a reason to slow down rather than a reason to skip the hostname check.
Final takeaway
The safest way to interpret playtime, playtimelogin, and www.playtime co.store is to treat them first as search strings. Before entering credentials, convert the result into a concrete technical question: what exact hostname is my browser connected to?
For Playtime Login readers, the durable routine is simple: use a known route, inspect the full registered domain, treat odd spacing or escaped punctuation as search syntax rather than proof of a URL, keep Safe Browsing enabled, and never let a familiar logo or HTTPS padlock substitute for destination verification.
Sources & Benchmark References
WHATWG — URL Standard: https://url.spec.whatwg.org/
ICANN — DNS Security Facilitation Initiative: look-alike domains and typosquatting: https://www.icann.org/en/system/files/files/dsfi-tsg-final-report-15oct21-en.pdf
ICANN — IDN Homograph Attacks: https://www.icann.org/en/announcements/details/icann-statement-on-idn-homograph-attacks-and-request-for-public-comment-23-2-2005-en
FTC — Online search results: the good, the bad, and the scammy: https://consumer.ftc.gov/consumer-alerts/2025/04/online-search-results-good-bad-scammy
FTC — How to Recognize and Avoid Phishing Scams: https://consumer.ftc.gov/articles/how-recognize-avoid-phishing-scams
Google Chrome Help — Manage warnings about unsafe sites: https://support.google.com/chrome/answer/99020
Google Search Console — Password reuse / phishing warnings: https://support.google.com/webmasters/answer/10887229
Playtime Login — homepage, used only as self-published brand context: https://playtimelogin.ph/
Playtime Login — Privacy Policy, used only as self-published brand context: https://playtimelogin.ph/privacy-policy/
Prior Playtime topic check — Task 191 covered passkeys and phishing-resistant authentication; Task 176 covered Incognito/shared computers; older work covered password-manager autofill.